

บัญชี Google Ads มี 2 ประเภท ได้แก่ บัญชีดูแลจัดการ Google Ads และ บัญชีผู้ลงโฆษณา Google Ads โปรดดูคำอธิบายโดยละเอียดเกี่ยวกับความสัมพันธ์ระหว่างคำเหล่านี้ กับคำอื่นๆ (เช่น บัญชีลูกค้าและลูกค้า) ได้ที่ ประเภทบัญชี
บัญชีดูแลจัดการสามารถจัดการบัญชีดูแลจัดการ Google Ads หรือบัญชีผู้ลงโฆษณา Google Ads อื่นๆ ได้ คุณสามารถลิงก์บัญชีผู้ลงโฆษณากับบัญชีดูแลจัดการ แล้วจัดการบัญชีผู้ลงโฆษณาผ่านบัญชีดูแลจัดการ โครงสร้างการลิงก์โดยรวมจะเป็นกราฟ แบบมีทิศทางและไม่มีวงจร โดยมีบัญชีผู้ลงโฆษณาอยู่ที่ระดับใบ (Leaf Level)
คุณสามารถให้สิทธิ์เข้าถึงบัญชี Google Ads แก่ผู้ใช้แต่ละรายหรือบัญชีบริการได้ โดยมี 2 วิธีในการให้สิทธิ์เข้าถึงบัญชีผู้ลงโฆษณาแก่ผู้ใช้ ดังนี้
- ให้สิทธิ์เข้าถึงบัญชีผู้ลงโฆษณาแก่ผู้ใช้โดยตรงด้วยการเชิญ ผู้ใช้เข้าสู่บัญชีดังกล่าว
- ให้สิทธิ์เข้าถึงบัญชีผู้ลงโฆษณาแก่ผู้ใช้โดยอ้อมด้วยการเชิญผู้ใช้เข้าสู่ บัญชีดูแลจัดการที่ลิงก์กับบัญชีดังกล่าว ผู้ใช้จะได้รับสิทธิ์เข้าถึงบัญชีผู้ลงโฆษณาเนื่องจากบัญชีดูแลจัดการมีสิทธิ์เข้าถึงบัญชีทั้งหมดที่ลิงก์ไว้ภายใต้บัญชีดูแลจัดการ
นอกจากนี้ คุณยังกำหนดบทบาทของผู้ใช้ได้เมื่อเชิญผู้ใช้ให้ จัดการบัญชี
ลองพิจารณาลำดับชั้นของบัญชีต่อไปนี้ สมมติว่าผู้ใช้ทุกคนมีสิทธิ์การเข้าถึงระดับมาตรฐาน
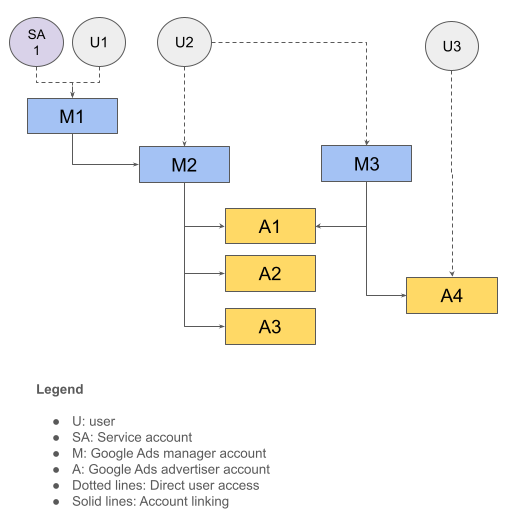
ตารางต่อไปนี้สรุปโครงสร้างบัญชีนี้
| ผู้ใช้ | มีสิทธิ์เข้าถึงโดยตรง | มีสิทธิ์เข้าถึงโดยอ้อม |
|---|---|---|
| U1, SA1 | M1 | M2, A1, A2, A3 |
| U2 | M2, M3 | A1, A2, A3, A4 |
| U3 | A4 |
รหัสลูกค้าสำหรับการเข้าสู่ระบบ
ผู้ใช้อาจมีสิทธิ์เข้าถึงลำดับชั้นของบัญชีหลายรายการ ในกรณีเช่นนี้ เมื่อทำการเรียก API คุณต้องระบุบัญชีรากที่จะใช้เพื่อกำหนดระดับการเข้าถึงบัญชีและการให้สิทธิ์อย่างถูกต้อง โดยให้ใส่ส่วนหัว login-customer-id ในคำขอ API
ตารางต่อไปนี้ใช้ลำดับชั้นของบัญชีจากตัวอย่างก่อนหน้าเพื่อแสดงรหัสลูกค้าสำหรับการเข้าสู่ระบบที่คุณใช้ได้ และรายการบัญชีที่เกี่ยวข้อง ซึ่งคุณสามารถเรียกใช้ได้
| ผู้ใช้ | รหัสลูกค้าสำหรับการเข้าสู่ระบบที่จะใช้ | บัญชีที่จะเรียกใช้ API |
|---|---|---|
| U1, SA1 | M1 | M1, M2, A1, A2, A3 |
| U2 | M2 | M2, A1, A2, A3 |
| U2 | M3 | M3, A1, A4 |
| U3 | A4 | A4 |
คุณข้ามการระบุส่วนหัว login-customer-id ได้หากผู้ใช้มีสิทธิ์เข้าถึงบัญชี Google Ads ที่คุณกำลังเรียกใช้โดยตรง เช่น คุณไม่จำเป็นต้องระบุส่วนหัว login-customer-id เมื่อใช้ข้อมูลเข้าสู่ระบบ U3 เพื่อเรียกใช้ A4 เนื่องจากเซิร์ฟเวอร์ของ Google Ads สามารถกำหนดระดับการเข้าถึงจากรหัสลูกค้า (A4) ได้อย่างถูกต้อง
หากคุณใช้ไลบรารีของไคลเอ็นต์ Google Ads API ให้ใช้การตั้งค่าต่อไปนี้เพื่อระบุส่วนหัว login-customer-id
Java
เพิ่มการตั้งค่าต่อไปนี้ลงในไฟล์ ads.properties
api.googleads.loginCustomerId=INSERT_LOGIN_CUSTOMER_ID_HERE
.NET
เพิ่มการตั้งค่าต่อไปนี้เมื่อเริ่มต้นออบเจ็กต์ GoogleAdsConfig และใช้เพื่อสร้างออบเจ็กต์ GoogleAdsClient
GoogleAdsConfig config = new GoogleAdsConfig()
{
    // ...
    LoginCustomerId = "INSERT_LOGIN_CUSTOMER_ID_HERE"
};
GoogleAdsClient client = new GoogleAdsClient(config);
Python
เพิ่มการตั้งค่าต่อไปนี้ลงในไฟล์ google-ads.yaml
login_customer_id: INSERT_LOGIN_CUSTOMER_ID_HERE
PHP
เพิ่มการตั้งค่าต่อไปนี้ลงในไฟล์ google_ads_php.ini
[GOOGLE_ADS]
loginCustomerId = "INSERT_LOGIN_CUSTOMER_ID_HERE"
Ruby
เพิ่มการตั้งค่าต่อไปนี้ลงในไฟล์ google_ads_config.rb
Google::Ads::GoogleAds::Config.new do |c|
  c.login_customer_id = 'INSERT_LOGIN_CUSTOMER_ID_HERE'
end
สร้างอินสแตนซ์ GoogleAdsClient โดยส่งเส้นทางไปยังตำแหน่งที่คุณเก็บไฟล์นี้
client = Google::Ads::GoogleAds::GoogleAdsClient.new(
  'path/to/google_ads_config.rb'
)
Perl
เพิ่มการตั้งค่าต่อไปนี้ลงในไฟล์ googleads.properties
loginCustomerId=INSERT_LOGIN_CUSTOMER_ID_HERE
curl
ระบุอาร์กิวเมนต์บรรทัดคำสั่งต่อไปนี้เมื่อเรียกใช้คำสั่ง curl
-H "login-customer-id: INSERT_LOGIN_CUSTOMER_ID_HERE"คุณสามารถใช้วิธี
CustomerService.ListAccessibleCustomers
เพื่อดึงข้อมูลรายการบัญชีที่ผู้ใช้มีสิทธิ์เข้าถึงโดยตรง
โดยบัญชีเหล่านี้สามารถใช้เป็นค่าที่ถูกต้องสำหรับส่วนหัว login-customer-id
Java
private void runExample(GoogleAdsClient client) { // Optional: Change credentials to use a different refresh token, to retrieve customers // available for a specific user. // // UserCredentials credentials = // UserCredentials.newBuilder() // .setClientId("INSERT_OAUTH_CLIENT_ID") // .setClientSecret("INSERT_OAUTH_CLIENT_SECRET") // .setRefreshToken("INSERT_REFRESH_TOKEN") // .build(); // // client = client.toBuilder().setCredentials(credentials).build(); try (CustomerServiceClient customerService = client.getLatestVersion().createCustomerServiceClient()) { ListAccessibleCustomersResponse response = customerService.listAccessibleCustomers( ListAccessibleCustomersRequest.newBuilder().build()); System.out.printf("Total results: %d%n", response.getResourceNamesCount()); for (String customerResourceName : response.getResourceNamesList()) { System.out.printf("Customer resource name: %s%n", customerResourceName); } } }
C#
public void Run(GoogleAdsClient client) { // Get the CustomerService. CustomerServiceClient customerService = client.GetService(Services.V25.CustomerService); try { // Retrieve the list of customer resources. string[] customerResourceNames = customerService.ListAccessibleCustomers(); // Display the result. foreach (string customerResourceName in customerResourceNames) { Console.WriteLine( $"Found customer with resource name = '{customerResourceName}'."); } } catch (GoogleAdsException e) { Console.WriteLine("Failure:"); Console.WriteLine($"Message: {e.Message}"); Console.WriteLine($"Failure: {e.Failure}"); Console.WriteLine($"Request ID: {e.RequestId}"); throw; } }
PHP
public static function runExample(GoogleAdsClient $googleAdsClient) { $customerServiceClient = $googleAdsClient->getCustomerServiceClient(); // Issues a request for listing all accessible customers. $accessibleCustomers = $customerServiceClient->listAccessibleCustomers(new ListAccessibleCustomersRequest()); print 'Total results: ' . count($accessibleCustomers->getResourceNames()) . PHP_EOL; // Iterates over all accessible customers' resource names and prints them. foreach ($accessibleCustomers->getResourceNames() as $resourceName) { /** @var string $resourceName */ printf("Customer resource name: '%s'%s", $resourceName, PHP_EOL); } }
Python
def main(client: GoogleAdsClient) -> None: customer_service: CustomerServiceClient = client.get_service( "CustomerService" ) accessible_customers: ListAccessibleCustomersResponse = ( customer_service.list_accessible_customers() ) result_total: int = len(accessible_customers.resource_names) print(f"Total results: {result_total}") resource_names: List[str] = accessible_customers.resource_names for resource_name in resource_names: # resource_name is implicitly str print(f'Customer resource name: "{resource_name}"')
Ruby
def list_accessible_customers() # GoogleAdsClient will read a config file from # ENV['HOME']/google_ads_config.rb when called without parameters client = Google::Ads::GoogleAds::GoogleAdsClient.new accessible_customers = client.service.customer.list_accessible_customers().resource_names accessible_customers.each do |resource_name| puts "Customer resource name: #{resource_name}" end end
Perl
sub list_accessible_customers { my ($api_client) = @_; my $list_accessible_customers_response = $api_client->CustomerService()->list_accessible_customers(); printf "Total results: %d.\n", scalar @{$list_accessible_customers_response->{resourceNames}}; foreach my $resource_name (@{$list_accessible_customers_response->{resourceNames}}) { printf "Customer resource name: '%s'.\n", $resource_name; } return 1; }
curl
# Returns the resource names of customers directly accessible by the user # authenticating the call. # # Variables: # API_VERSION, # OAUTH2_ACCESS_TOKEN: # See https://developers.google.com/google-ads/api/rest/auth#request_headers # for details. # curl -f --request GET \ "https://googleads.googleapis.com/v${API_VERSION}/customers:listAccessibleCustomers" \ --header "Content-Type: application/json" \ --header "Authorization: Bearer ${OAUTH2_ACCESS_TOKEN}" \
ฉันควรทำอย่างไรหากวิธี ListAccessibleCustomers ไม่ดึงข้อมูลรหัสลูกค้าของฉัน
หากวิธี CustomerService.ListAccessibleCustomers
ไม่ดึงข้อมูลรหัสลูกค้าที่คุณคาดว่าจะปรากฏในผลลัพธ์
สาเหตุที่เป็นไปได้มีดังนี้
คุณมีสิทธิ์เข้าถึงรหัสลูกค้า แต่สิทธิ์เข้าถึงดังกล่าวออกให้ผ่านบัญชีดูแลจัดการระดับบน ตัวอย่างเช่น หากคุณเรียกใช้วิธี
ListAccessibleCustomersด้วยข้อมูลเข้าสู่ระบบของผู้ใช้U1ในตัวอย่างก่อนหน้า วิธีนี้จะแสดงเฉพาะM1ในผลลัพธ์ แม้ว่าU1จะมีสิทธิ์เข้าถึงบัญชีอื่นๆ ก็ตาม หากต้องการยืนยันความเป็นไปได้นี้ ดึงข้อมูล ลำดับชั้นของบัญชีโดยเรียกใช้searchหรือsearchStreamคิวรีกับแหล่งข้อมูลcustomer_clientสำหรับบัญชีแต่ละบัญชีที่ วิธีListAccessibleCustomersแสดงผล โดยให้ตั้งค่าบัญชีแต่ละบัญชีเหล่านี้เป็นlogin-customer-idตามที่อธิบายไว้ใน ส่วนก่อนหน้า หากคุณมีสิทธิ์เข้าถึงบัญชีเป้าหมาย คุณจะดึงข้อมูลบัญชีดังกล่าวเป็นส่วนหนึ่งของลำดับชั้นของบัญชีรายการใดรายการหนึ่งได้คุณใช้ข้อมูลเข้าสู่ระบบ OAuth ไม่ถูกต้อง สถานการณ์ที่พบบ่อยที่สุดคือคุณใช้ข้อมูลเข้าสู่ระบบของผู้ใช้รายอื่น เช่น อาจเกิดจากการผสมข้อมูลเข้าสู่ระบบของ Sandbox หรือนักพัฒนาแอปกับข้อมูลเข้าสู่ระบบจริงโดยไม่ได้ตั้งใจ หรืออ่านข้อมูลเข้าสู่ระบบของผู้ใช้รายอื่นจากฐานข้อมูลหรือแคชในเครื่องอย่างไม่ถูกต้อง วิธีแก้ปัญหาที่เป็นไปได้วิธีหนึ่งสำหรับ ปัญหานี้คือใช้ Google People API เพื่อดึงข้อมูลชื่อและ อีเมลของผู้ใช้ที่เข้าสู่ระบบ แล้วตรวจสอบว่าตรงกับอีเมล ที่คุณคาดไว้หรือไม่
คุณไม่มีสิทธิ์เข้าถึงบัญชี โปรดทำตามคู่มือ การเข้าถึงบัญชีเพื่อรับสิทธิ์เข้าถึงบัญชีลูกค้าที่ถูกต้อง
บทบาทของผู้ใช้
Google Ads API ไม่มีโมเดลการเข้าถึงแยกต่างหากของตัวเอง หรือใช้ขอบเขต OAuth 2.0 แยกต่างหากเพื่อจำกัดฟังก์ชันการทำงาน เช่น Google Ads API ใช้ขอบเขตเดียวกันสำหรับการดำเนินการอ่านอย่างเดียวเทียบกับการดำเนินการอ่านและเขียน แต่ Google Ads API จะใช้บทบาทของผู้ใช้
แบบเดียวกับที่ Google Ads รองรับ เมื่อมีการมอบบทบาทของผู้ใช้ให้กับบัญชีที่ระดับดูแลจัดการ บัญชีในลำดับชั้นจะรับบทบาทดังกล่าว หากผู้ใช้มีบทบาทที่ขัดแย้งกันในบัญชีหนึ่งๆ ระบบจะแก้ไขระดับที่ถูกต้องโดยใช้บัญชี login-customer-id ที่ระบุไว้ในคำขอ API
ตารางต่อไปนี้ใช้ลำดับชั้นของบัญชีจากตัวอย่างก่อนหน้าและแสดงผลของการมอบบทบาทของผู้ใช้ต่างๆ ให้กับผู้ใช้
| ผู้ใช้ | บทบาทของผู้ใช้ที่มอบให้ | login-customer-id | ระดับการเข้าถึงที่มีผล |
|---|---|---|---|
| SA1 | สิทธิ์การเข้าถึงระดับมาตรฐานในบัญชี M1 | M1 | สิทธิ์การเข้าถึงระดับมาตรฐานใน M1, M2, A1, A2, A3 |
| U2 |
สิทธิ์เข้าถึงระดับมาตรฐานใน M2 สิทธิ์การเข้าถึงระดับอ่านอย่างเดียวใน M3 |
M2 | สิทธิ์การเข้าถึงระดับมาตรฐานใน M2, A1, A2, A3 |
| U2 |
สิทธิ์เข้าถึงระดับมาตรฐานใน M2 สิทธิ์การเข้าถึงระดับอ่านอย่างเดียวใน M3 |
M3 | สิทธิ์การเข้าถึงระดับอ่านอย่างเดียวใน M3, A1, A4 |